
Label Studio vulnerable to Cross-site Scripting if `` or `` are used in labeling config
### Summary On all Label Studio versions prior to 1.11.0, data imported via file upload feature is not properly sanitized prior to being rendered within a [`Choices`](https://labelstud.io/tags/choices) or [`Labels`](https://labelstud.io/tags/labels) tag, resulting in an XSS vulnerability. ### Details Need permission to use the "data import" function. This was reproduced on Label Studio 1.10.1. ### PoC 1. Create a project. 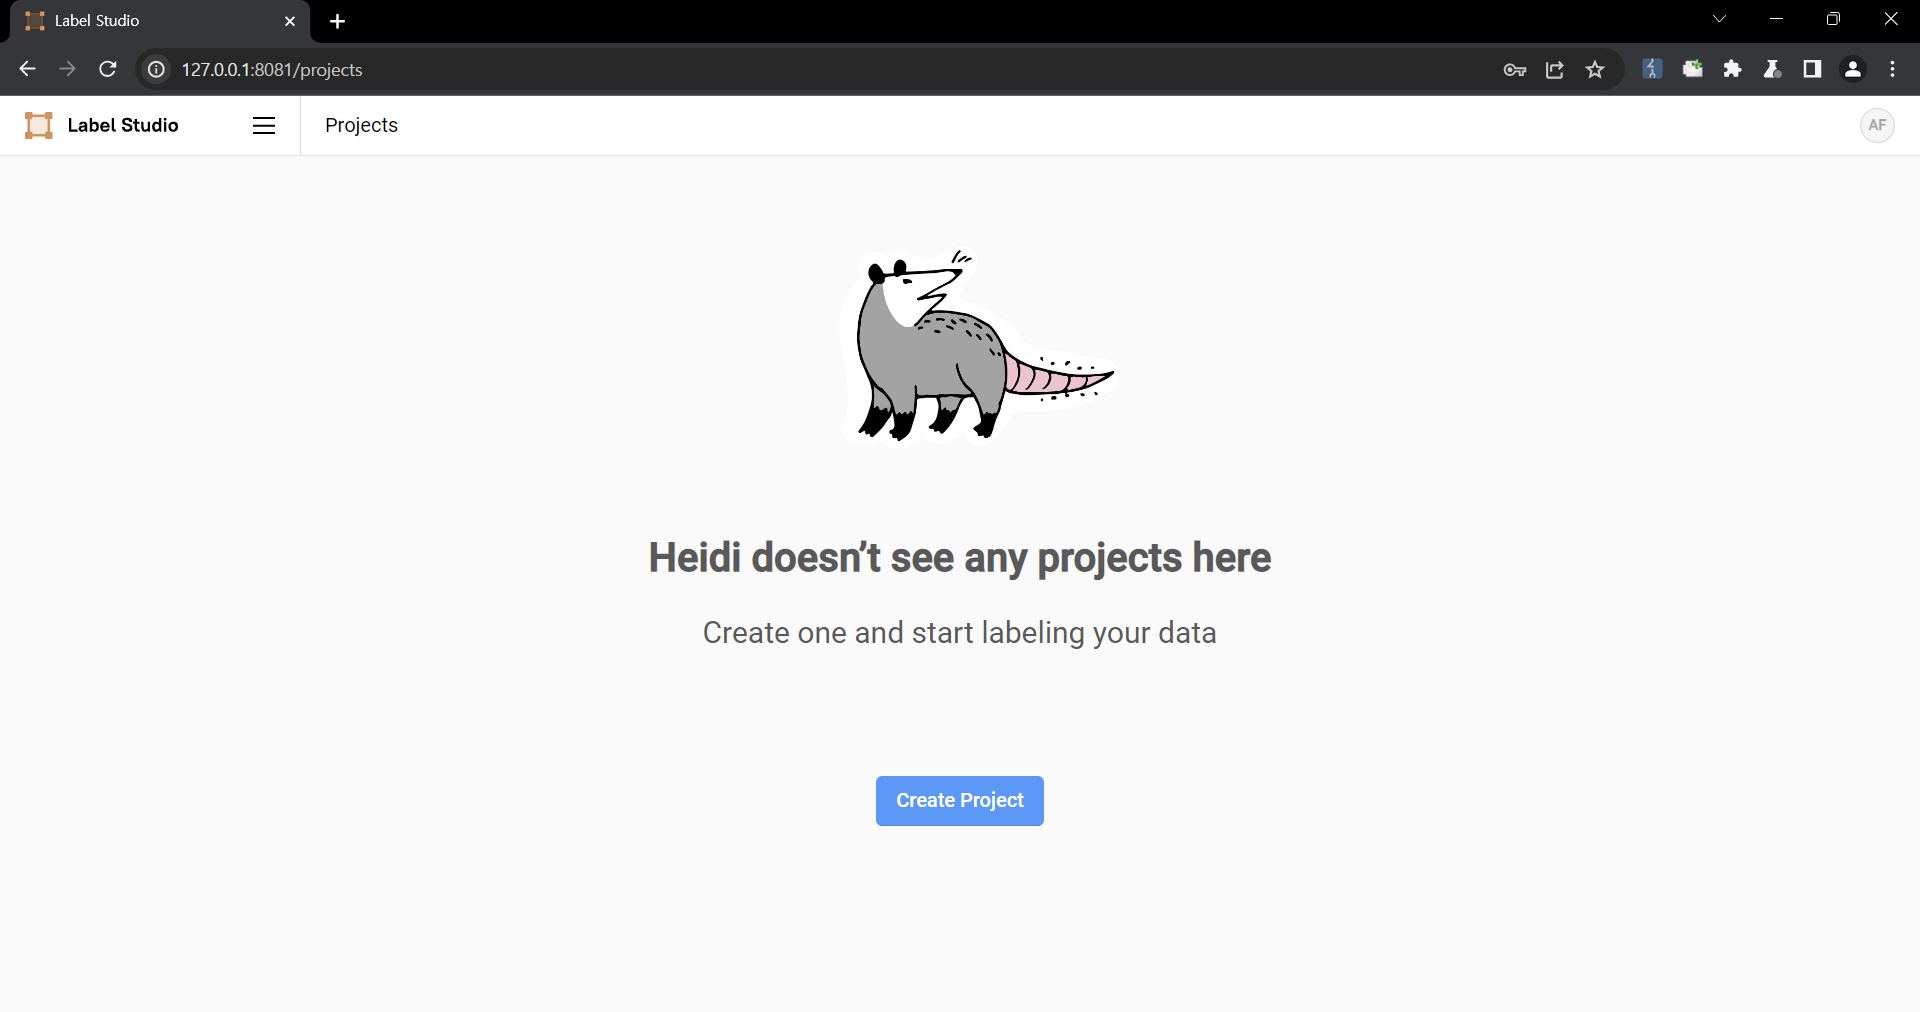 2. Upload a file containing the payload using the "Upload Files" function. 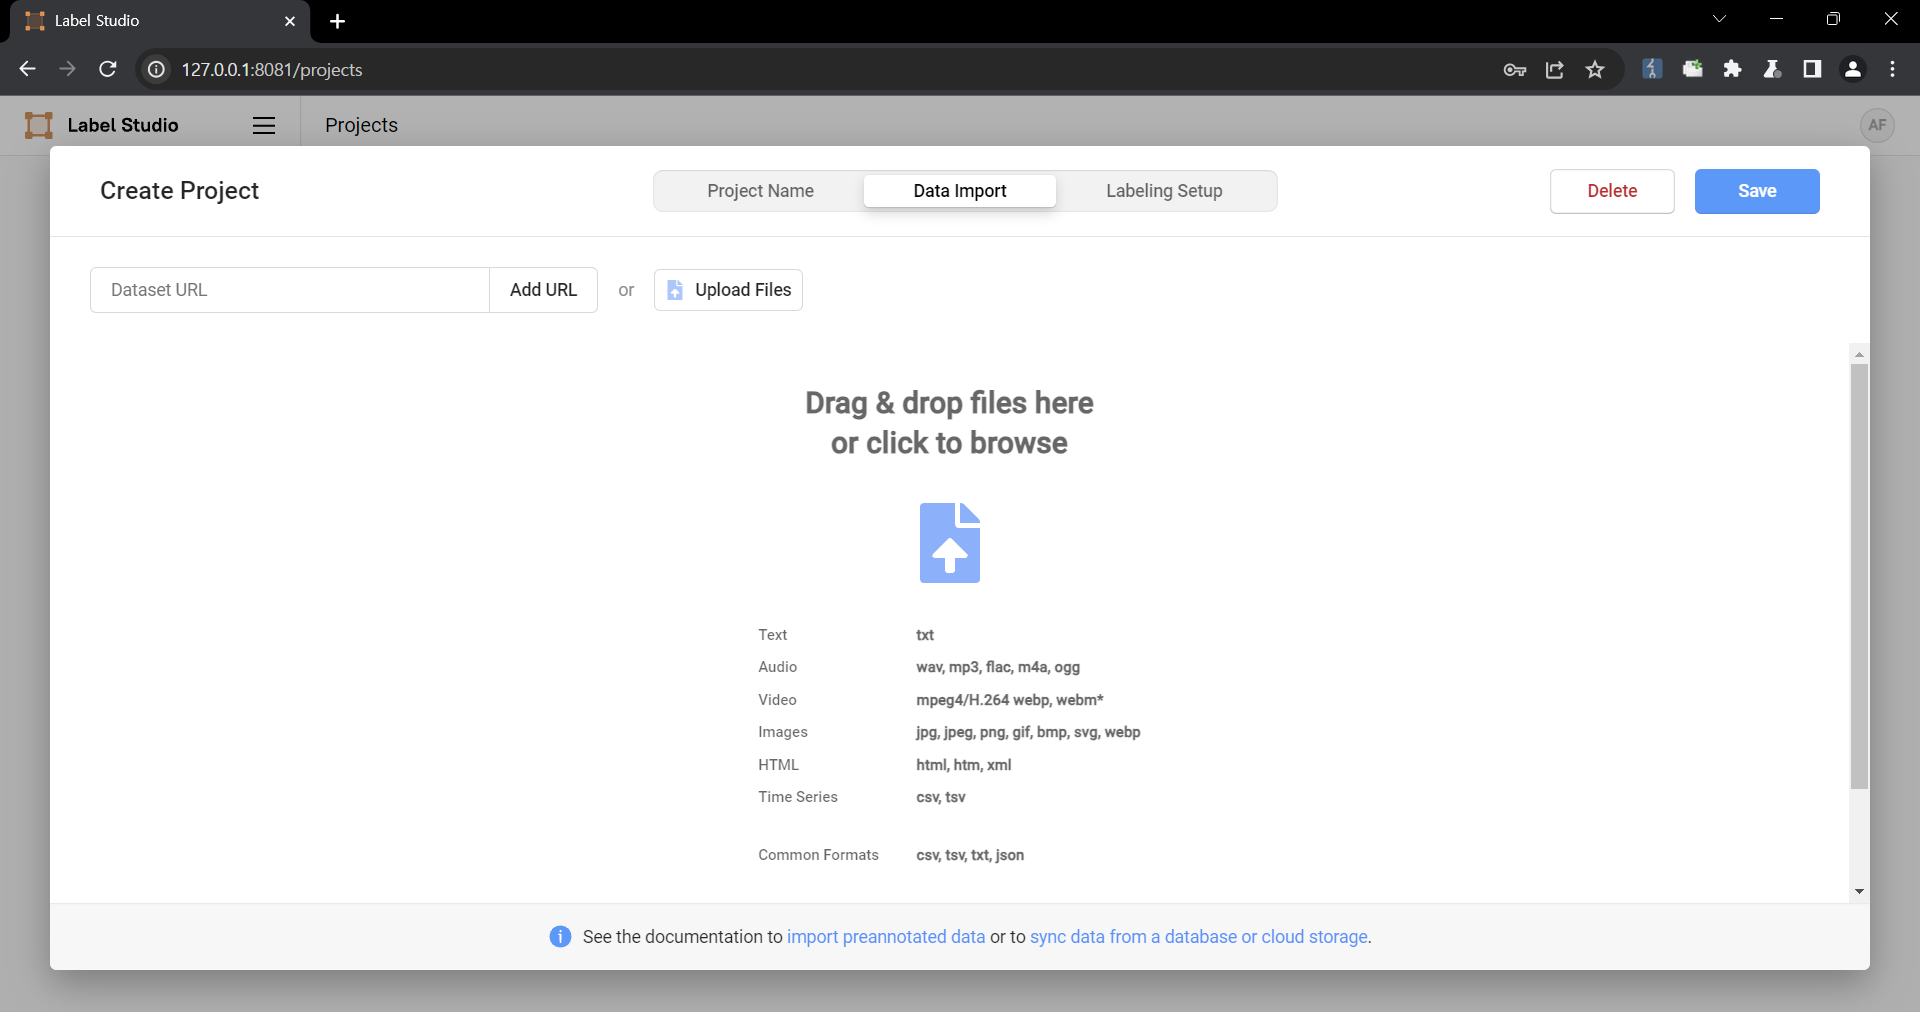 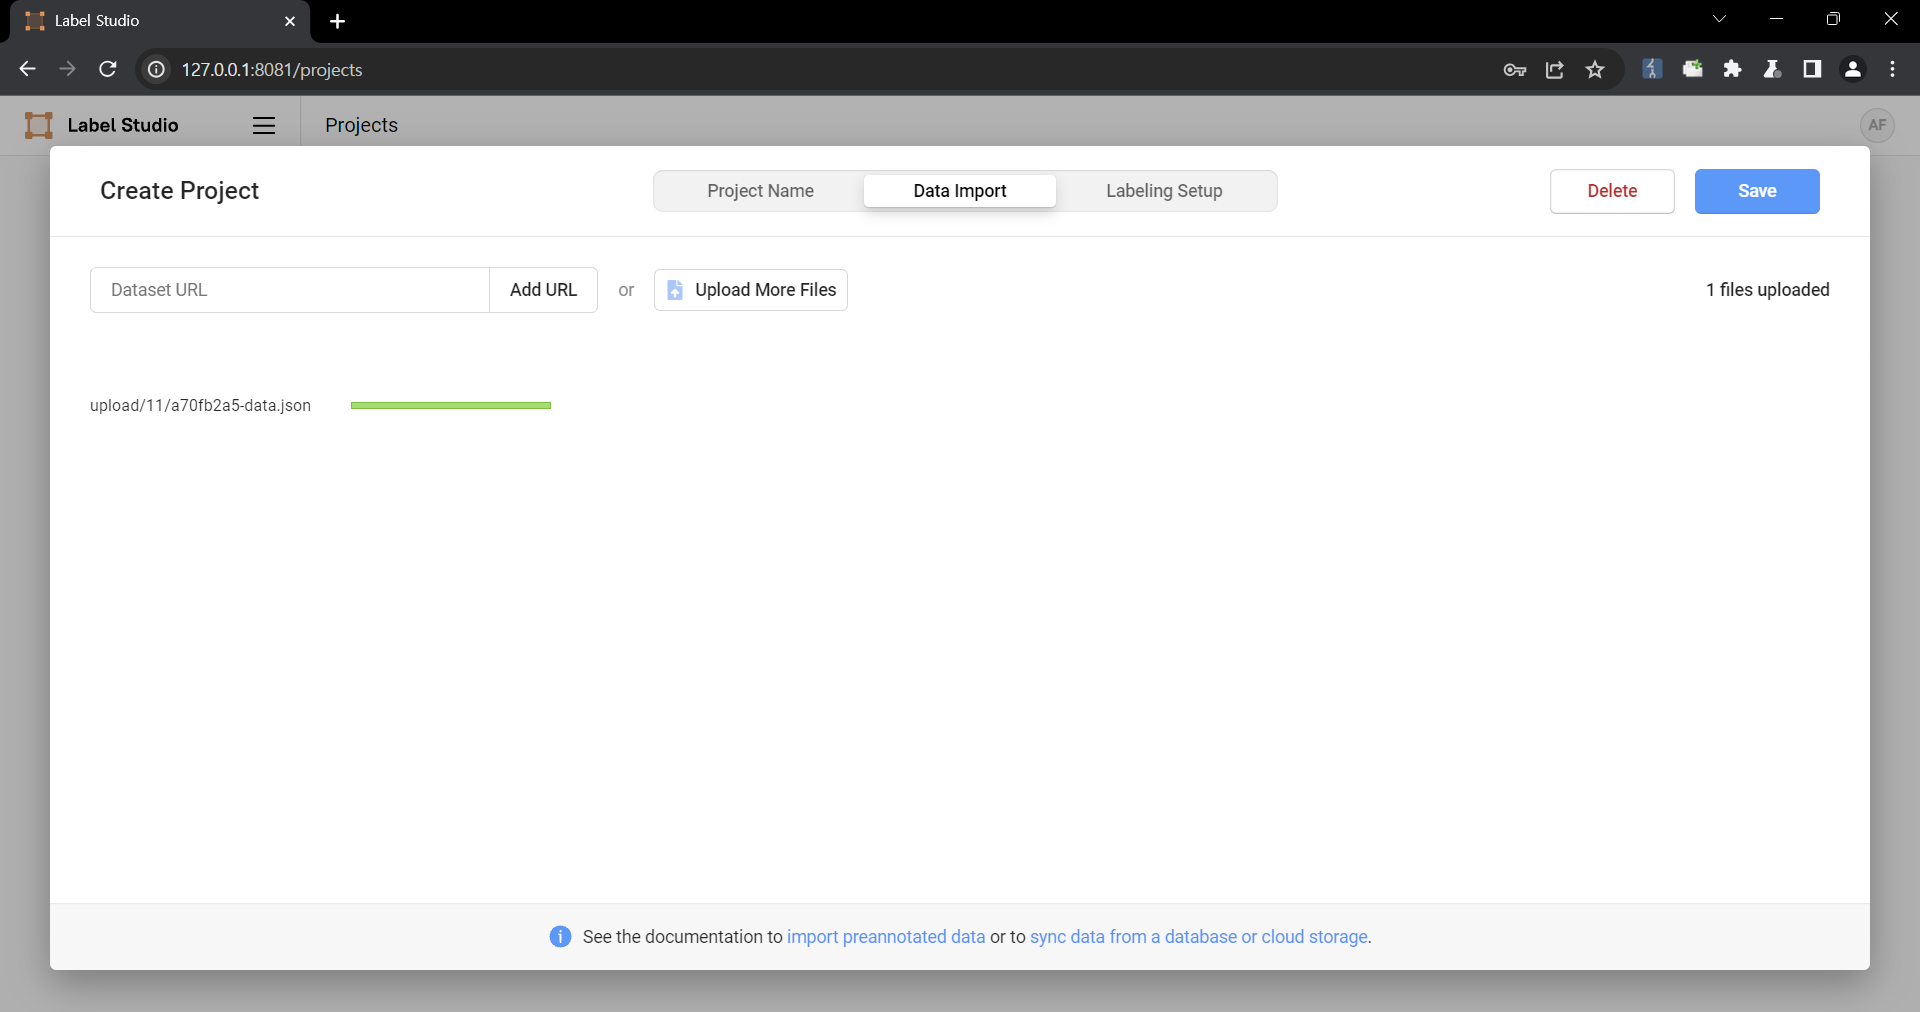 The following are the contents of the files used in the PoC ``` { "data": { "prompt": "labelstudio universe image", "images": [ { "value": "id123#0", "style": "margin: 5px", "html": "" } ] } } ``` 3. Select the text-to-image generation labeling template of Ranking and scoring 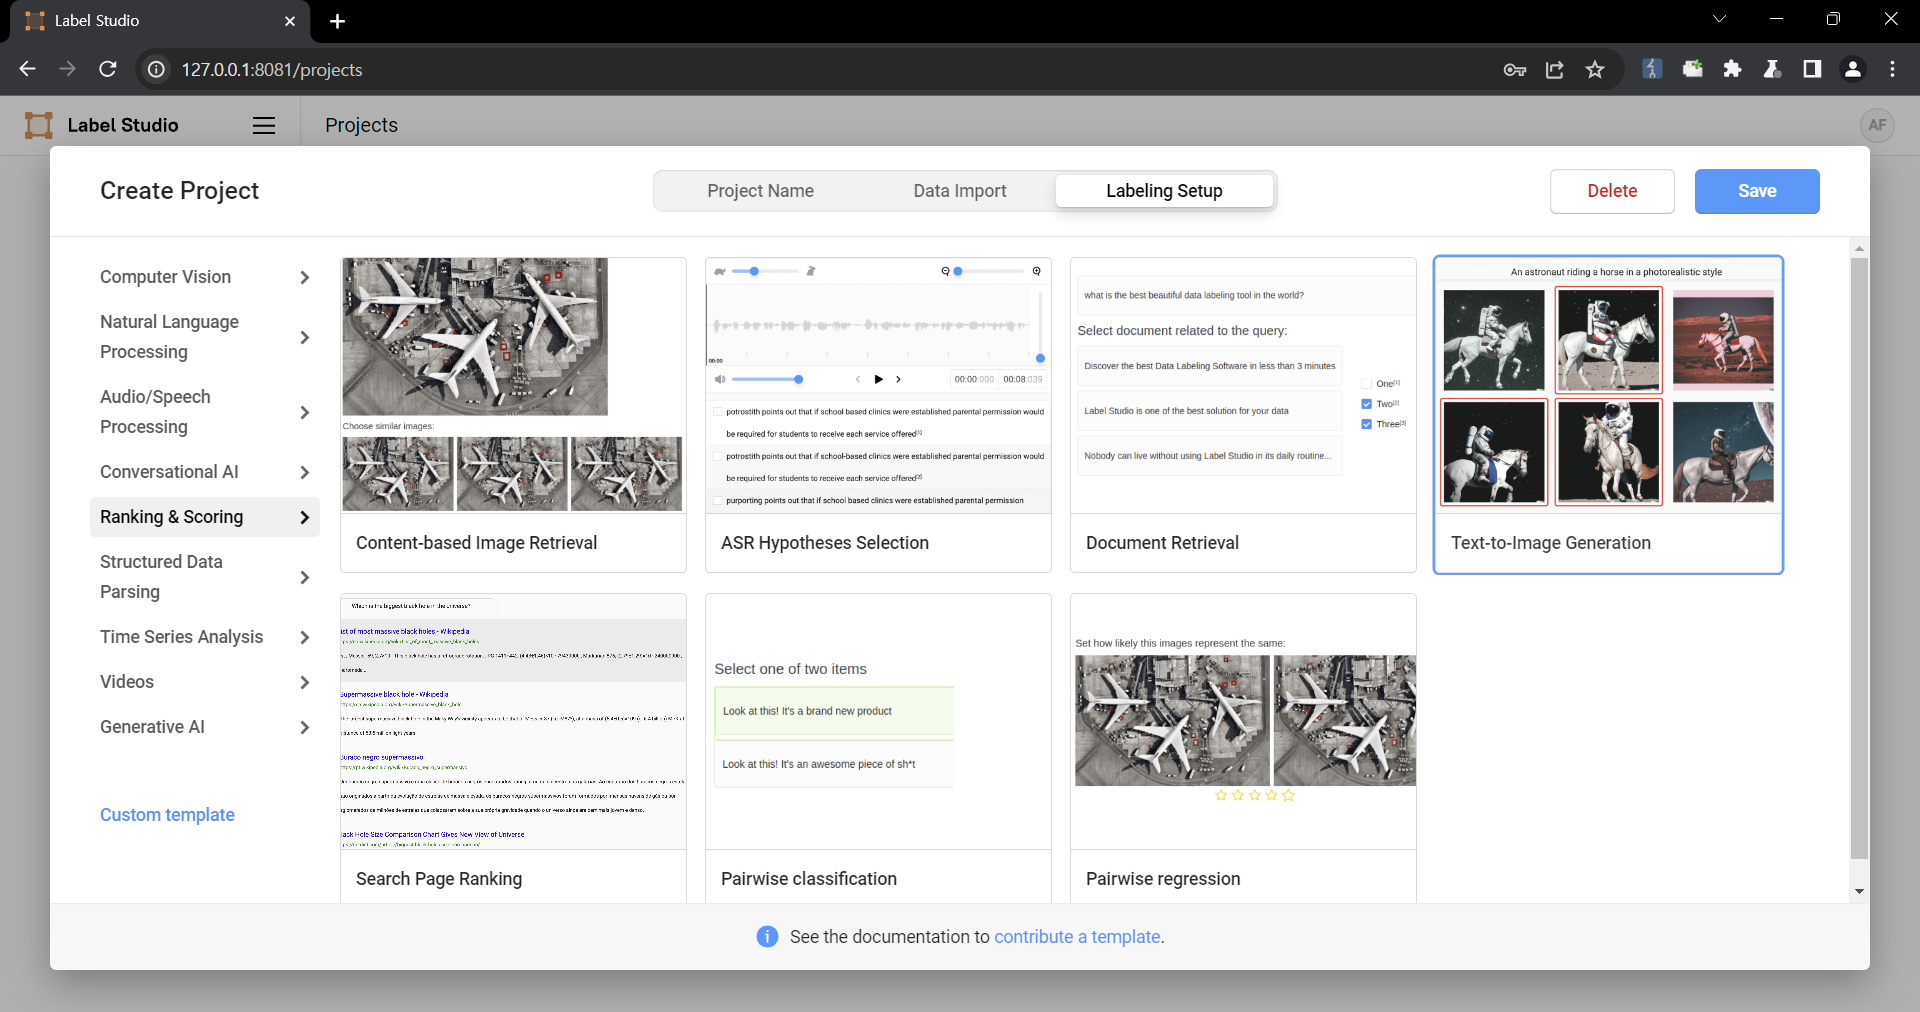 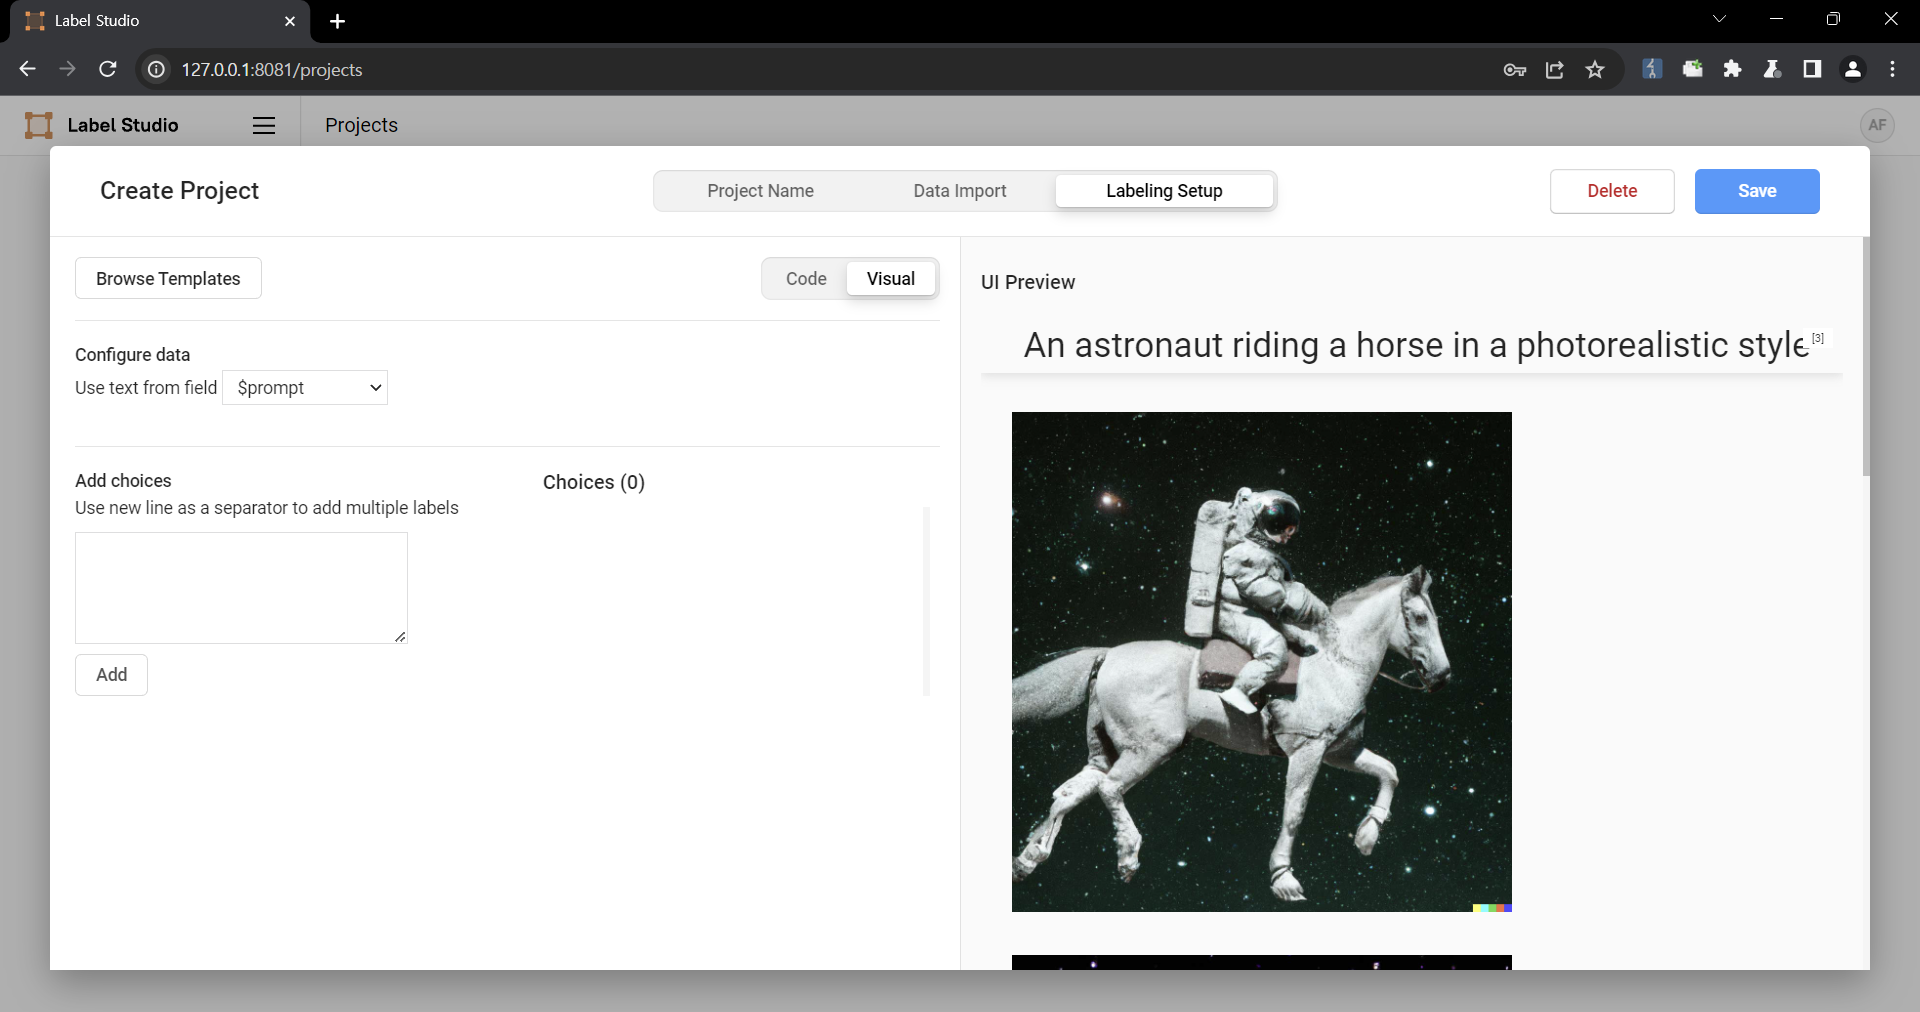 4. Select a task ![4 Select a task]
- Products
- Not specified
- Affected versions
- Not specified
- Fixed versions
- Not specified
- CVEs
- CVE-2024-26152
- Confirmed fixed CVEs
- Not specified
- Updated in this feed
- 5 Nov 2026, 05:41 UTC · Revision 1
Source evidence
Label Studio vulnerable to Cross-site Scripting if `` or `` are used in labeling config
core-osv · Original sourcePublished 22 Feb 2024, 21:52 UTC
### Summary On all Label Studio versions prior to 1.11.0, data imported via file upload feature is not properly sanitized prior to being rendered within a [`Choices`](https://labelstud.io/tags/choices) or [`Labels`](https://labelstud.io/tags/labels) tag, resulting in an XSS vulnerability. ### Details Need permission to use the "data import" function. This was reproduced on Label Studio 1.10.1. ### PoC 1. Create a project.  2. Upload a file containing the payload using the "Upload Files" function.   The following are the contents of the files used in the PoC ``` { "data": { "prompt": "labelstudio universe image", "images": [ { "value": "id123#0", "style": "margin: 5px", "html": "" } ] } } ``` 3. Select the text-to-image generation labeling template of Ranking and scoring   4. Select a task ![4 Select a task]
osv:CVE-2024-26152
Complete source record
{
"id": "d37f020cf158434fd8e185715ee00eca64e57a7e653a6e5378ffeb536d79656a",
"url": "https://osv.dev/vulnerability/CVE-2024-26152",
"method": "structured",
"payload": {
"kind": "advisory",
"title": "Label Studio vulnerable to Cross-site Scripting if `` or `` are used in labeling config",
"summary": "### Summary On all Label Studio versions prior to 1.11.0, data imported via file upload feature is not properly sanitized prior to being rendered within a [`Choices`](https://labelstud.io/tags/choices) or [`Labels`](https://labelstud.io/tags/labels) tag, resulting in an XSS vulnerability. ### Details Need permission to use the \"data import\" function. This was reproduced on Label Studio 1.10.1. ### PoC 1. Create a project.  2. Upload a file containing the payload using the \"Upload Files\" function.   The following are the contents of the files used in the PoC ``` { \"data\": { \"prompt\": \"labelstudio universe image\", \"images\": [ { \"value\": \"id123#0\", \"style\": \"margin: 5px\", \"html\": \"\" } ] } } ``` 3. Select the text-to-image generation labeling template of Ranking and scoring   4. Select a task ![4 Select a task]",
"evidence": "osv:CVE-2024-26152",
"products": [],
"severity": "medium",
"structured": {
"id": "CVE-2024-26152",
"aliases": [
"CVE-2024-26152",
"GHSA-6xv9-957j-qfhg",
"PYSEC-2024-249"
],
"metrics": [
{
"type": "CVSS_V3",
"score": "CVSS:3.1/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:N/A:N"
}
],
"affected": [
{
"ranges": [
{
"repo": "https://github.com/humansignal/label-studio",
"type": "GIT",
"events": [
{
"introduced": "0"
},
{
"fixed": "a9766f0325bd99ff2339ffa8a7988a66383c0f8d"
},
{
"fixed": "5df9ae3828b98652e9fa290a19f4deedf51ef6c8"
}
],
"database_specific": {
"extracted_events": [
{
"cpe": "cpe:2.3:a:humansignal:label_studio:*:*:*:*:*:*:*:*",
"range": [
{
"introduced": "0"
},
{
"fixed": "1.11.0"
}
],
"source": "CPE_RANGE"
},
{
"range": [
{
"fixed": "5df9ae3828b98652e9fa290a19f4deedf51ef6c8"
}
],
"source": "REFERENCES_COMMIT"
},
{
"range": [
{
"fixed": "a9766f0325bd99ff2339ffa8a7988a66383c0f8d"
}
],
"source": "REFERENCES_TAG",
"original_tag": "1.11.0"
}
]
}
}
],
"versions": [
"v1.4.1",
"v1.4.0",
"v1.3.0",
"v1.2.0",
"v1.1.1",
"v1.1.0",
"v1.0.2",
"v1.0.1",
"v1.0.0",
"v0.9.1.post1",
"v0.9.1.post0",
"v0.9.0.post5",
"v0.9.0.post4",
"v0.9.0.post3",
"v0.9.0",
"v0.8.2",
"v0.8.1",
"v0.8.0",
"v0.7.5.post0",
"v0.7.3",
"v0.7.2",
"v0.7.1",
"v0.7.0",
"v0.6.1",
"v0.6.0",
"v0.5.1",
"v0.4.8",
"v0.4.7",
"v0.4.6",
"v0.4.5",
"v0.4.4",
"v0.4.0",
"v0.3.0",
"v0.2.2",
"v.0.2.1-8",
"v.0.2.1-5",
"v.0.2.1-4",
"v.0.2.1-3",
"v.0.2.1-2",
"v.0.2.0",
"v.0.1.6",
"v.0.1.5",
"v.0.1.4",
"v.0.1.2",
"v.0.1.1",
"v.0.1.0"
],
"database_specific": {
"source": "https://storage.googleapis.com/cve-osv-conversion/osv-output/CVE-2024-26152.json"
}
}
],
"modified": "2026-10-28T02:30:43.104630388Z",
"provider": "osv",
"references": [
"https://github.com/HumanSignal/label-studio/releases/tag/1.11.0",
"https://github.com/CVEProject/cvelistV5/tree/main/cves/2024/26xxx/CVE-2024-26152.json",
"https://github.com/HumanSignal/label-studio/security/advisories/GHSA-6xv9-957j-qfhg",
"https://nvd.nist.gov/vuln/detail/CVE-2024-26152",
"https://github.com/HumanSignal/label-studio/commit/5df9ae3828b98652e9fa290a19f4deedf51ef6c8",
"https://github.com/HumanSignal/label-studio/pull/5232"
],
"provider_metadata": {
"cwe_ids": [
"CWE-79"
],
"cna_assigner": "GitHub_M",
"osv_generated_from": "https://github.com/CVEProject/cvelistV5/tree/main/cves/2024/26xxx/CVE-2024-26152.json"
}
},
"related_cves": [
{
"value": "CVE-2024-26152",
"evidence": "/id"
}
],
"security_relevant": true,
"severity_evidence": "/severity/0/score"
},
"source_id": "core-osv",
"document_id": 510778,
"published_at": "2024-02-22T21:52:26.193+00:00"
}